



Critical Security Apparatus on Apple’s Hide My Email Feature
Automatically translated
 Writer
Apple’s privacy feature Hide My Email, known for more than a year, but not covered with vulnerability I came to my day. Open worked on all of the addresses that are tried in limited tests and led to the fact email address behind the secret address with open identification search tools to everyone. Leak was stored in 550 5.7.1 and 552 5.7.0 rejecting codes that servers rotate.
The actual email address of users in specific scenarios was becoming open to third parties. After the finding is independently verified, Apple’s privacy promises have been reputed. Hide My Email is one of the privacy tools that enable users to register on apps and websites without sharing real addresses in Apple ecosystem.
How Does Hide Work My Email Feature?
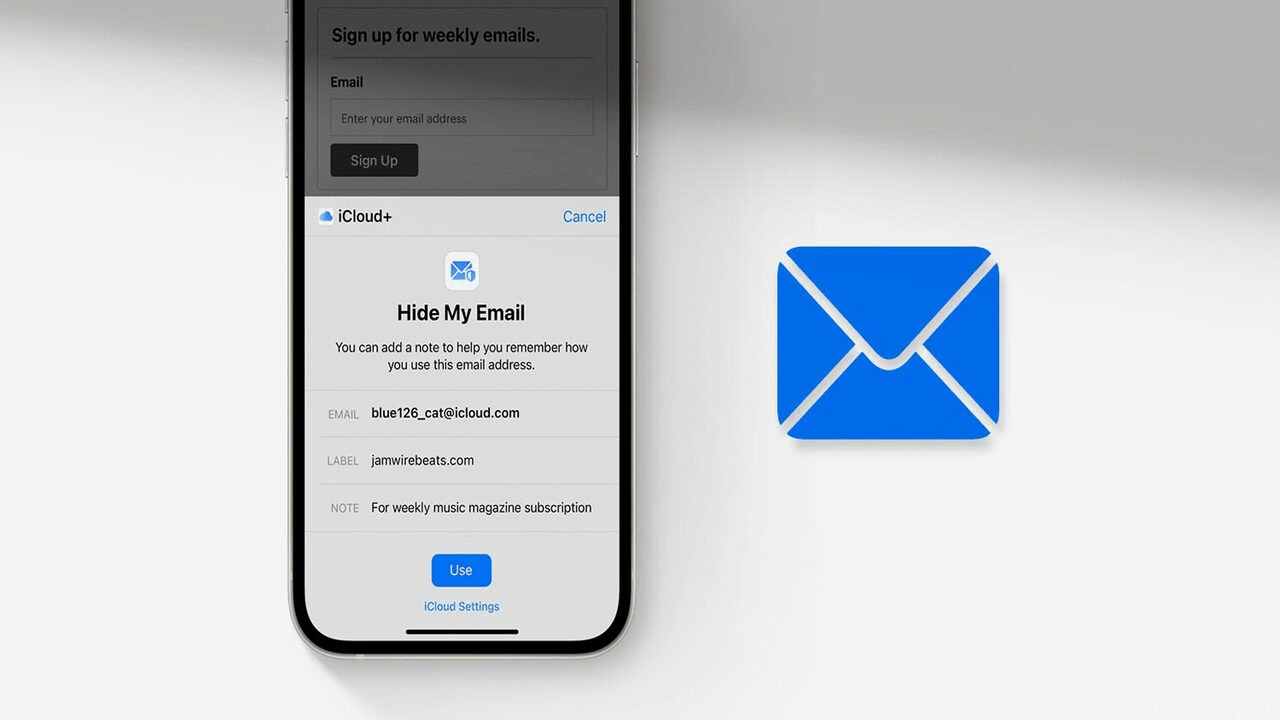
Hide My Email from iCloud+ subscription produces a random nickname on the user name. Sites and applications only see this temporary address. The incoming messages are redirected through Apple’s servers, and the user falls on the actual frombox. The user can disable the generated address by one click, the messages from that address are also cut. The aim is to prevent personal information from sharing unnecessary location when signing up for online services.
What Does the Safety Problem Cover?
The system was not working as expected in specific usage scenarios, and the actual email address of the user has become visible. Name that reveals the connection, EasyOptOuts The founder of the company Tyler Murphy was. Murphy reported the problem for the first time on 13 June 2025 to Apple, told step by step how the deficit can regenerate. Apple has received a review and reported that the problem in March 2026 is completely resolved. Murphy’s re-tests were still unclosed. Murphy findings after the months to be a change Mobile Media moved to the technology publication called.
404 Media confirmed the topic by testing on one of the Hide My Email addresses. EasyOptOuts has released all the vulnerability with sample error messages.
The problem was hidden in Email Rejection Records
Open was caused by Apple’s e-mail routing system to put the secret address into that message while returning server error message in some cases. When a message sent to the nickname was rejected, the record was able to reveal the actual address behind it. According to Murphy’s transfer, this situation was asking users who rely on privateness to hide from spammers or data collectors.
Apple Island Two Stage Patch Covered
Apple moved to the public after the vulnerability was announced. A partial correction on July 2, 2026 published an additional fix on July 7. The company’s vulnerability has reported that it was previously covered in 3 March and 30 June 2026, but two trials also received trouble. Apple domain name of Hide My Email addresses in a separate step icloud.comFrom private.icloud.comHe heard that he would be able to move to ', in the year he will combine domain names with Sign In with Apple.
What risks of the patch are closed, which they take:
Risk | How to create | Stop after patch m |
|---|---|---|
Dissolving the real address | The server rejecting record turned the actual address with the nickname | 7 days After July 2026, closed in the addresses produced |
Trace of old nickname addresses | The actual address can be matched with the nickname inserting in mail transfer records | 7 days It takes for addresses before July, these addresses are no more anonymous |
Targeting in data breaches | No. of solved addresses marked the user directly in breach of the registered service | Current as long as old addresses are not changed |
Hide from data collectors | Can be found by matching users who produce addresses by trusting the property | It takes for old addresses, closed in new addresses |
Abuse in the past | Open remained open for a long time than three months, there is no registration on which it resolves | Not knowing, Apple did not share data on it |
Bulk Case Process Started
After the announcement of the opening, the public case against Apple was opened. Anthony Alvarez’s return to iCloud+ subscription fees in the case opened on July 15, 2026. Petition, although Apple has been informed for more than a year, the feature does not disable, warn users and update privacy statements.
What Does Users Change For?
Hide My Email announced in 2021 is offered as a feature that requires iCloud+ subscription. It was expected to block unwanted emails and data collectors. After the last patch, it is reported that the problem is closed for the nicknames produced. It is not known if the previously created addresses are not abused in the past.
Why Important For iCloud Security Users?
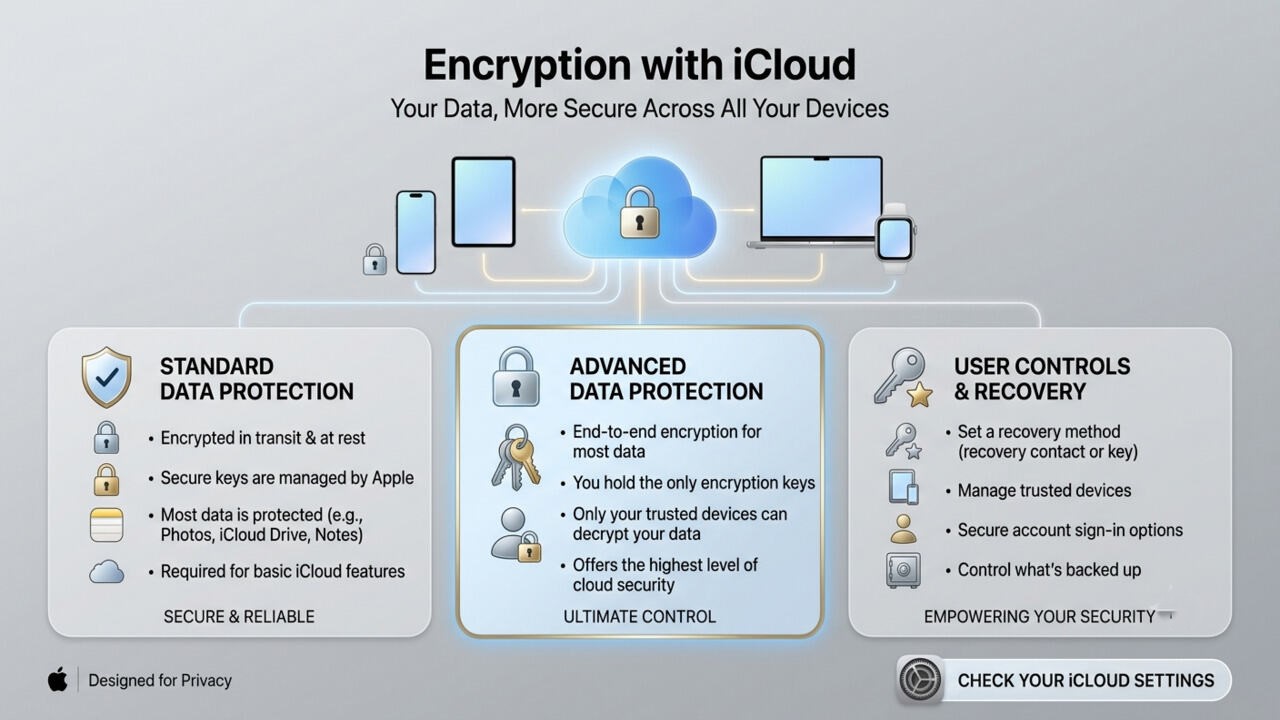
iCloud does not only provide email service. Photos, documents, contacts, notes and device backups are kept under the same account. The following steps are recommended for account security:
Enable two-factor authentication k
Powerful and unique choice of Apple ID password
To regularly check the connected devices
Follow suspicious login notifications
Unused Hide disable My Email addresses
Review iCloud account settings at regular intervals
Apple’s 7 is reported that leakage is closed for addresses produced after July patch. The remaining question is that the vulnerability has been resolved by who of these addresses for twelve months when it is open. The course of the Alvarez case can also reveal the first concrete data on that period.
WriterHindistan Kendi Yapay Zeka Yasası İçin Hazırlığa Başlıyor
WWII UFO Raporları Ortaya Çıktı


