



AI Cyber Attack Threat Companies Keep In Alarm
Automatically translated
 Admin
A financial employee of Arup in February 2024 transferred to foreign accounts of 25 million dollars belonging to the company. All of the managers on the screen were cloned by AI; it was not possible to distinguish the voice, facial expression and mimics from each other. This is not a single exception. Artificial intelligence-supported cyber attacks reached a new threshold with a number of 28 million cases on a global scale. The AI cyber attack threat is no longer just a technical problem; it has become a field that requires corporate authentication, financial approval processes and re-identification of human trust. In this article, the most up-to-date data of 2026 addresses concrete cases and corporate defense methods.
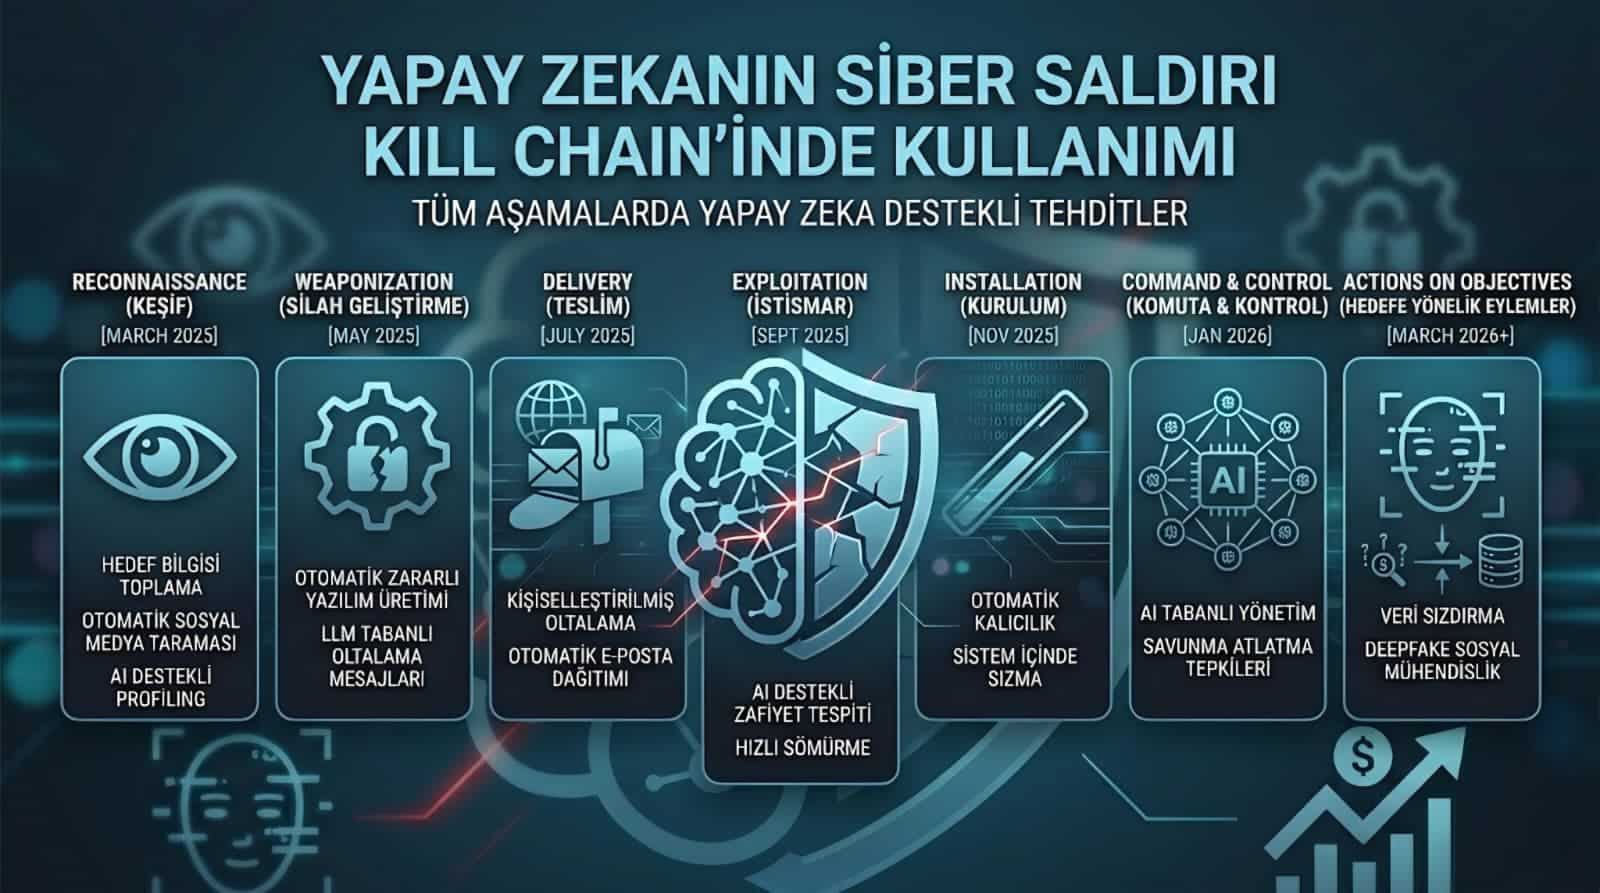
Artificial Intelligence Residual Attacks
Cyber attacks have been performed with human power for a long time, time-consuming and error-open operations. To prepare a phishing message, it would be that weeks are spent to explore the target system and terminate the failure. This table has changed.
Kaspersky Research and Development Group Manager Vladislav Tushkanov is currently using threats actors for major language models (LLM) code writing, infrastructure installation and automation of operational processes. The production of harmful components from the discovery stage of the Kill chain is supported by AI every step from poor screenings to commissioning vehicles.
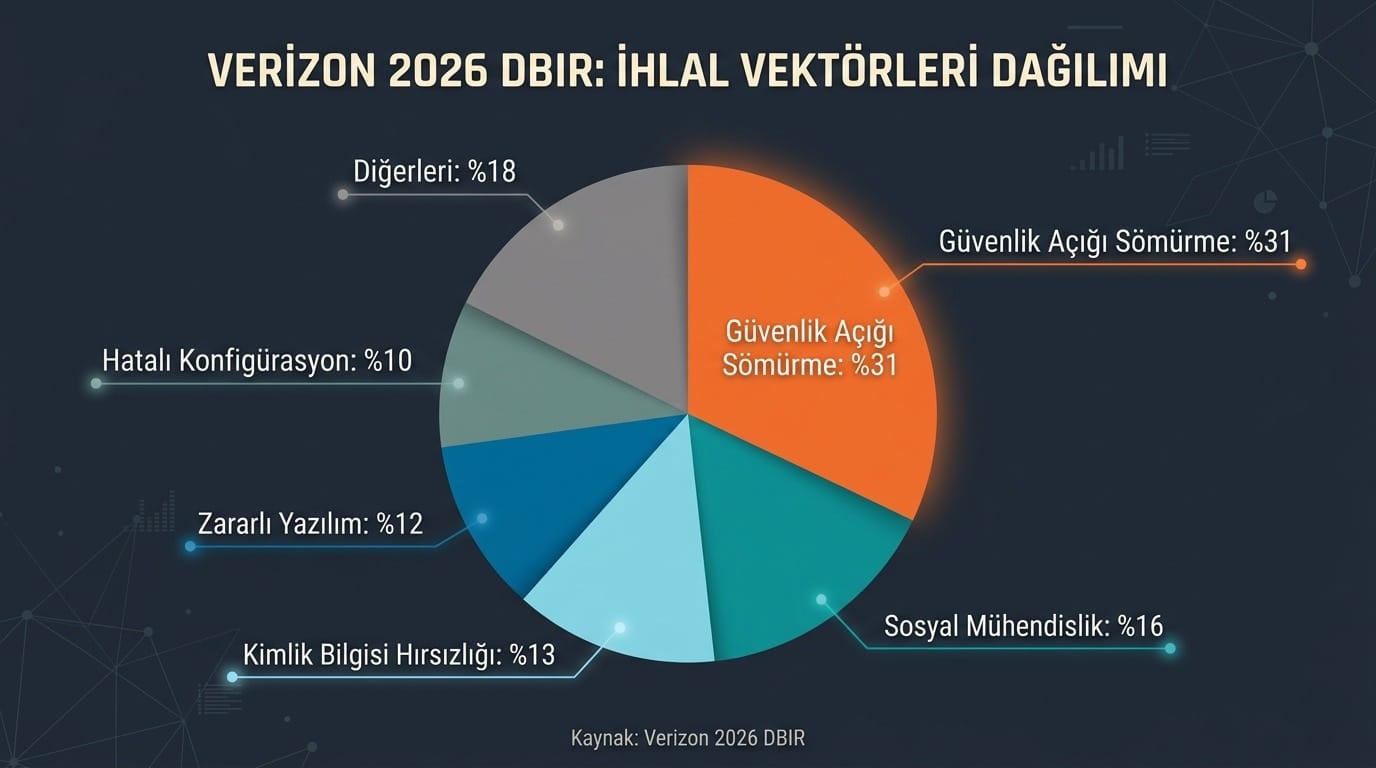
Verizon’s 2026 DBIR report This year prepared was placed in a detailed bull: attackers are downloading time from months to time between vulnerability and abuse using AI. For institutions, this means that the intervention window is seriously narrowed, regardless of how quickly the patching process is executed.
Attacks are not only starting with the choice of goals. AI also comes into action to hide traces that are used after the completion of the attack. This situation significantly makes judicial review processes.
How does Deepfake and Social Engineering Work?
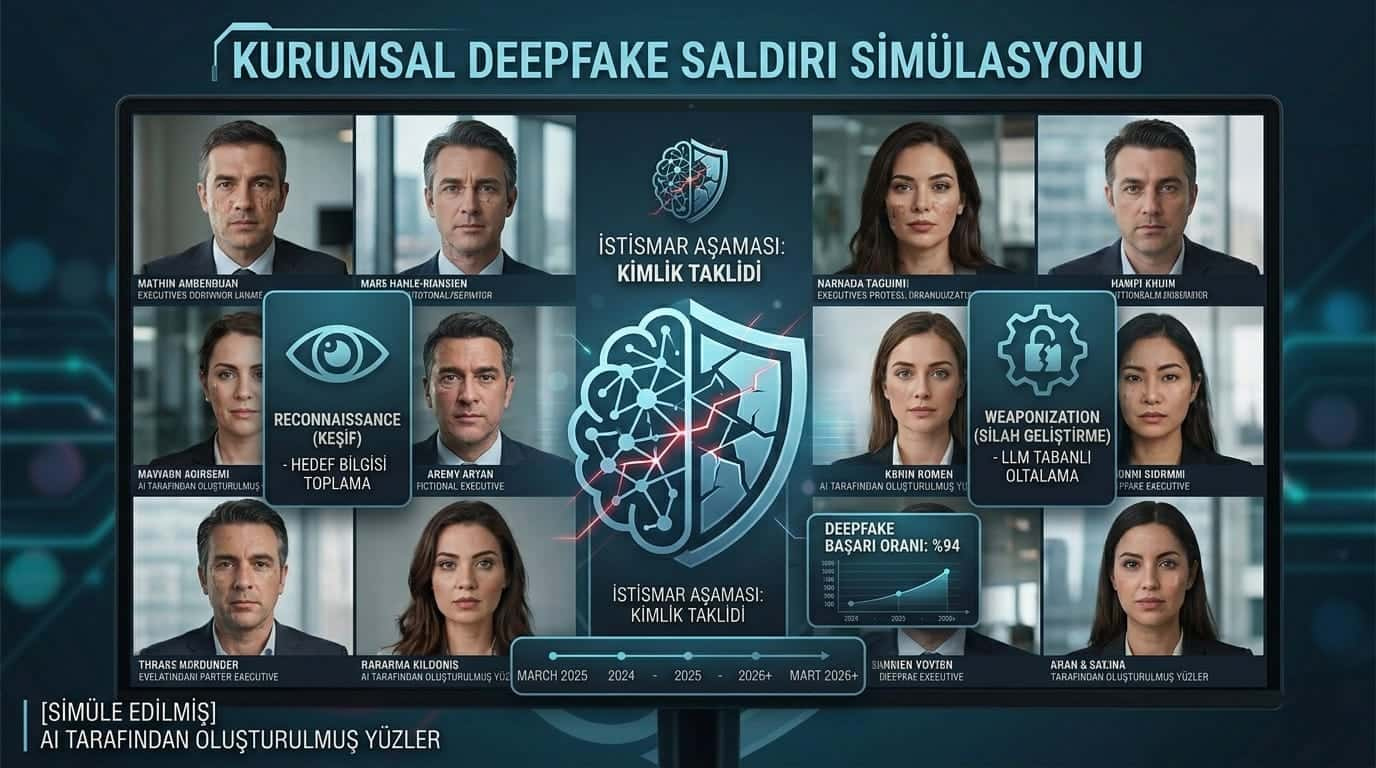
In addition to hardware or software deficit, human element always kept an important place among cyber attack vectors. With artificial intelligence, this element has become much more reliable and scalable.
In the case of Arup, which took place in February 2024, the attackers cloned the voice and image of the company CFO and the top managers through public material. No one on the screen was real at the meeting of the employee involved. 25,6 million dollars transfer order was given in no questioned sualless.
This case is not exception. LastPass data breachAfter that, in another attack for the company, we tried social engineering on a employee by cloned the voice of the threat actors from Karim Toubba via WhatsApp. The trial was noticed due to excessive severity and unusual communication channel. Wiz CEO Assaf Rappaport TechCrunch Discrupt 2024He announced the public that the group of employees target deepfake attacks.
In 2025, FBI officially announced phishing campaigns that mimic the top-level authorities in the US with AI audio cloning. Voice messages aim to create a sense of ivediness, using confidence.
According to the research published in SoSafe on February 2026 in social engineering, institutions remain still insufficient against these tactics. Only 39% of companies evaluate their ability to identify against AI-supported attacks as high or very high.
2026 AI Cyber Threat Table With Figures
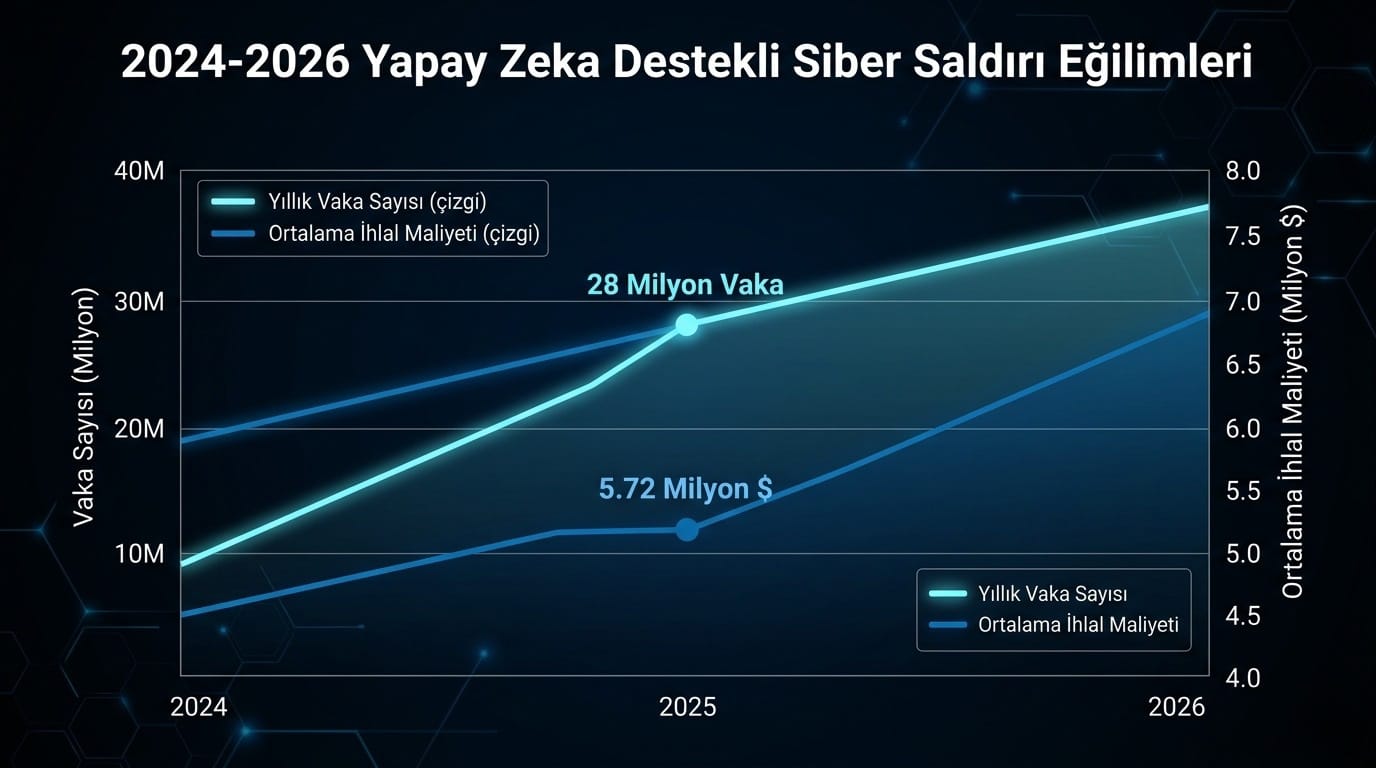
Numbers beyond case samples clearly reveal how big the table is.
According to the 2026 DBIR report that Verizon published this year 31,000 incidents analyzed in 145 countries and 22.000 verified violations were reviewed. This comes almost twice the last year.
Metric | Value | Source |
|---|---|---|
AI phishing click rate | %54 | DeepSafe / SoSafe 2025 |
Traditional phishing click rate | %12 | DeepStrike 2025 |
AI-supported average breach cost Home | 5,72 million dollars | IBM 2025 |
Deepfactor increase rate (2022-2025) | %2.137 | McAfee / iProov 2025 |
The share of ransomware in all violations | %48 | Verizon DBIR 2026 |
AI attack of institutions | %87 | Cisco 2025 |
The situation on the phishing side is particularly remarkable. According to the Microsoft Cyber Signals 2025 report, the AI production phishing content increased by 46% compared to one year ago. The 82,6% of existing phishing emails are now created using AI; this rate was around 54% a year ago.
A different table appears on the Ransomware side. According to Verizon 2026 DBIR, ransom software attacks are located in 48% of all violations, but the average payout is back to 139.975 in 2025 from 177.614 dollars in 2023. The victims are now paying less or refused to offer. However, attacks did not stop, the targets have changed.
What Are the New Risks Expecting Companies?
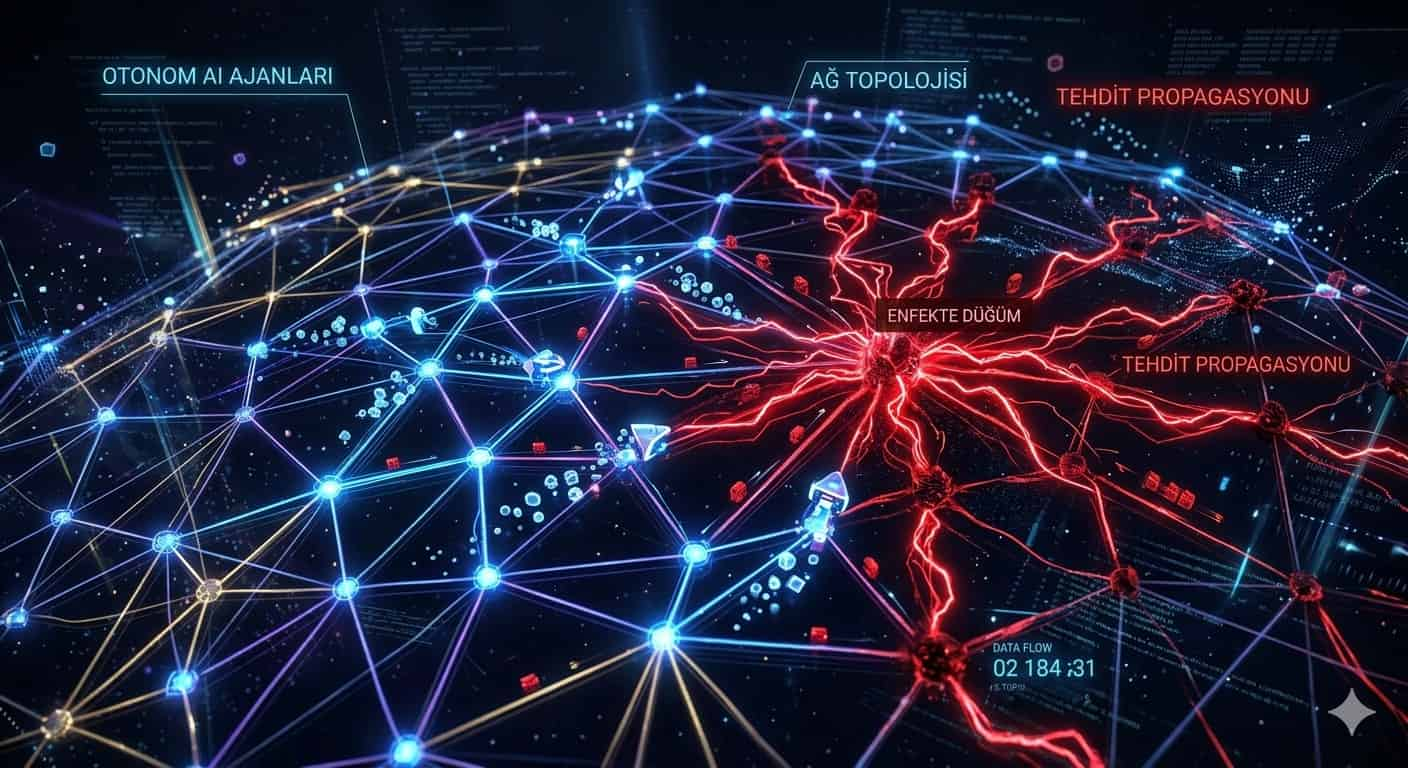
Deepfake and phishing are now known threats. There are three more domains that need to be understood: agencyal AI attacks, shadow AI and biometric targeting.
Fortinet’s 2026 Cyber Threat Forecasts Report As the Transfer of Insurance NewspaperIt is noted that a lot of based agencyal AI will begin to change direction. Attack agents in this model are distributed to multiple goals, adapts to defenders reactions and coordinates the task in half autonomously.
Shadow AI turned into a different concern in the industry. Practical DevSecOps's 2026 AI Security Statistics Report According to the institutions 68% of AI vehicle use suffered from the leak of data, but only 23% have a formal policy that prevents it. This problem was defined as "shadow AI" in Verizon 2025 DBIR and 72% of company employees were taken into account to access AI platforms with corporate email accounts.
Biometric targeting is also added to the table. In a period where the fingerprint began to replace the passwords of facial recognition and retina data, Bitdefender Turkey distributor Laykon Informatics Operations Director Flame Akkoyunlu announced that this area has become a number of targets for 2026.
OWASP LLM Top 10 prompt injection reached its first position in 2025. NIST reports show that the AI-specific CVE number has increased over two thousand percent since 2022.
What is the Status on the Defense Side?
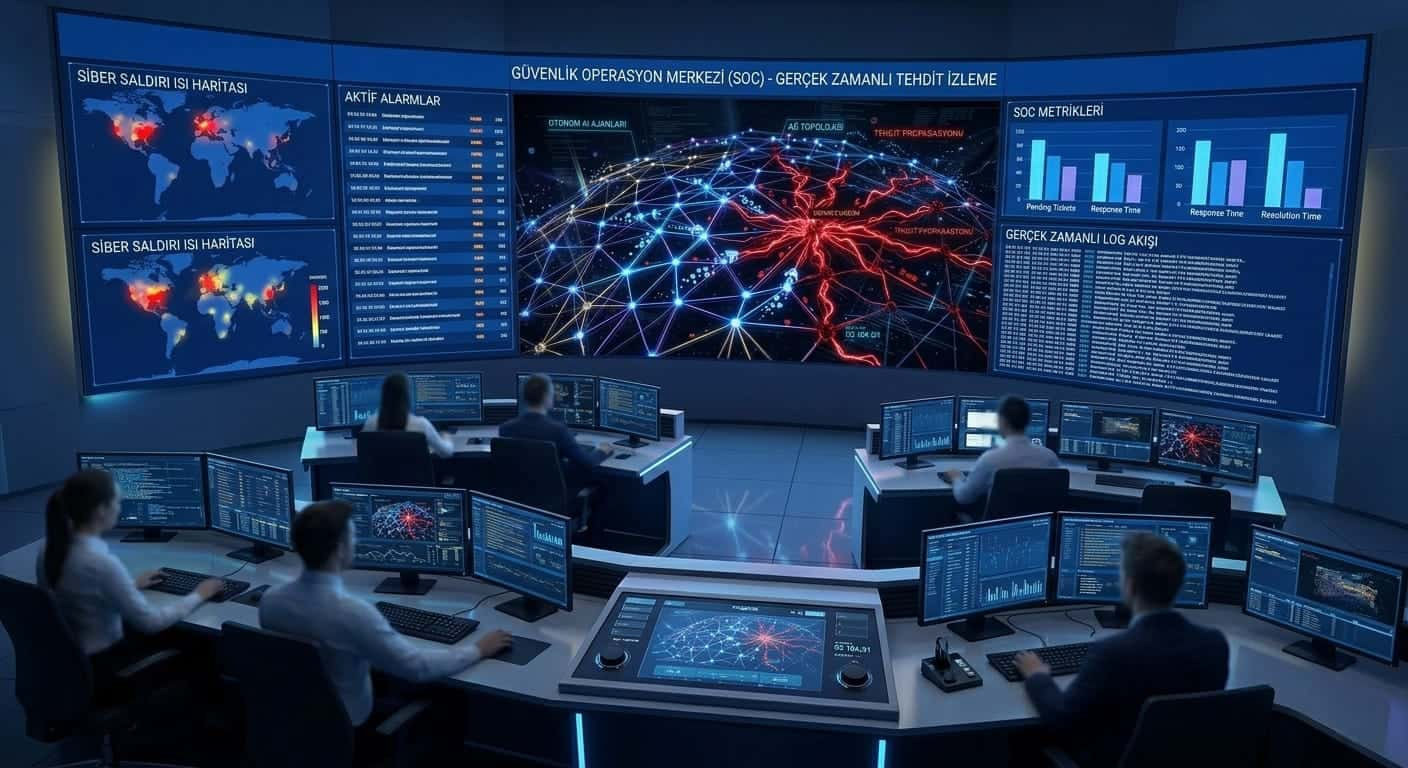
If the AI was stronger on the attack side, it also provides concrete benefits for institutions on the defense side. However, institutions that benefit from this benefit are still in minority.
According to IBM’s 2026 data, companies using AI and automation are downloading the breach cost of 3,62 million dollars. In companies that do not use AI, this figure is 5,52 million dollars. The difference between 1.9 million dollars. Practical DevSecOps report According to the AI-supported security teams, the average threat detection time (MTTD) reduces the manual scan load 60% when shortening 50%.
Indicator |
|---|
AI Supported Defense
AI-Free Defense
Average breach cost Home
3,62 million dollars
5,52 million dollars
Violation shutdown time
108 days faster
Close Tags
Detection time (MTTD)
50% shorter
Close Tags
Manual scan loading
60% less Tags
Close Tags
However, deficiencies continue. According to Verizon 2026 DBIR, institutions patch only 26% of the known abused security statements (KEV) catalog; this rate was 38% a year ago. Standard patching time is 43 days after 32 days.
What Is the Table in Turkey?
Global data is serious; but a special assessment to Turkey is also necessary to understand the table.
As Anadolu Agency transfers A cyber security company manager expresses that advanced identification has increased the impact of methods such as personalized oltama messages and automated malware development and "2025's decisive trend". Corporate security now stresses that it should be defined as a service that requires 24/7 monitoring, not as a software purchase.
According to December 2025 estimates of Bitdefender Turkey, 2026 will be the year that deepfake pluglidinin became undisable in live negotiations on platforms such as Zoom and Teams. The scams can request money transfer by mimicting company managers or family members’ face and voice simultaneously. This table starts a new era, which should be activated by predefined security passwords, not only "see" in financial approval processes.
Kaspersky’s December 2025 estimates reveal that AI traces on the attack side will strengthen the analysis. This situation in digital economies such as Turkey, dangers of harmful artificial intelligence models Increasing corporate awareness is more critical.
For those who wonder the technical dimensions of artificial intelligence security A large frame is presented in this field; whether AI systems are hackable and protected layers are addressed.
What does the community think?
Supporters
Security researchers argue that AI would be a big bug to ignore the value it adds to the defending side. While SOC teams are strong to deal with an average of 4.484 per day, they were observed that the fake positive rate drops seriously when supported with AI. It is reported that those who adopt automation approach have "more threat with less vehicles". Verizon and IBM provide data to this approach.
News
The opposite opinion is concentrated at this point: AI does not eliminate inequalities because it also shares the same tools as aggressive as it is useful for the defender. Even strong attacks of actors with low technical skills are opened. The threat ecosystem of this situation presented as "Democraticization". The agencyal AI attacks are predicted to consolidate this round.
Frequently Asked Questions
What is AI cyber attack? AI cyber attack is the name given to the types of attacks used for one or multiple stages, such as discovering the tools of artificial intelligence, plan attack, create malicious software or victim manipulate meat. The difference from traditional attacks is the automation level and adaptability capacity; AI is significantly difficult to detect as it can change the plug according to the defense response.
How does Deepfake attack work? Saldurganlar creates a clone from the public audio or image material of the target person. This clone can be used in a video conference participant, WhatsApp voice or phone call. The victim does not hesitate to comply with the instruction when he encounters the voice and image of the familiar person. Arup and LastPass cases are concrete examples of this mechanism.
How can companies protect from AI cyber attacks? Multi-factor authentication in the first step should not be counted only for sound or image-based transactions; pre-determined verification passwords should be applied. In the second step, SOC teams should be equipped with AI-supported detection tools, they should be abandoned manually dealing with warning volumes. Employees in the third step should undergo regular training on deepfake and AI phishing.
How much is the cost of AI cyber attacks? According to IBM’s 2025 data, the average cost of a AI-supported data breach reached 5,72 million dollars; this figure rose 13% per previous year. The damages caused by cyber crime globally exceeded 30 billion dollars in 2025; in 2026, the global cost is expected to approach 15 trillion dollars.
What is the relationship between Ransomware and AI? Based on the 2026 report of Practical DevSecOps, 41% of the available ransomware families contain AI components for adaptive attack delivery. Critical steps such as attack timing, target priorities and defense jump are optimized with AI. Verizon 2026 DBIR drops the average amount of ransom while showing that all violations are ransomware in 48%; the victims are increasingly paid or have no edema.
What is Shadow AI and why is dangerous? Shadow AI expresses applications that employees access AI tools through their personal accounts or unsupervised platforms outside the official corporate policy. Verizon 2025 DBIR determined that employees using AI in corporate devices have made it with corporate email accounts. This may result in the flow of sensitive business data into uncontrolled AI platforms.
The official publication of 2026 DBIR is discussed in the industry as the largest diameter document, which is released by the AI-supported attack trend. The AI usage of threat actors by partnering with Verizon team Anthropic shows how seriously the table is monitored. The response window measured with old months is now calculated with hours. It is necessary to adjust the speed of the defending side accordingly.
 Admin
AI Reklam Görselleri Güven Sorununu Büyütüyor
Reflex Robotics: Depodan Ev İşlerine Robotik Devrim


