



How to Recover VS Code Cyber Attack GitHub?
Automatically translated
 Admin
eight minutes. A harmless extension when a developer is installed on VS Code, has dealt about 3.800 GitHub internal storage in a short time. This attack conducted by TeamPCP group in May 2026 proved with concrete figures how developer tools are a security blind point. The chronology of the attack in this article, the technical methods used are addressing who target the group for 2026 and what the developers can do against this threat.
3.800 Warehouse in 18 Minutes: What’s Age?
18 May 2026, clock 12:30 UTC. The 18.95.0 version of the Nx Console Visual Studio Code extension was released on the official VS Code Marketplace. The extension was in 2,2 million installation and verified broadcast status. After eight minutes, at 12:48, Nx team detected and removed the malicious version.
It may seem like a late answer. However, this 18 minutes was really late as a GitHub employee had enough to build the extension. GitHub detected an internal breach on May 19 and detected on May 20 News published in Tom's Hardware announced the public. The company noted that the violation of the official statement on X is corrected, isolates the affected device and immediately rotates the critical credentials.
The hacker group called TeamPCP was previously moved. Breached cyber crime forum was claimed to be accessed at 4,000 private GitHub store and was asked at least 50,000 dollars for the resource code that was stolen. The description of the group was drawn a clear line: "This is not a ransom request." The purpose was not to squeeze GitHub directly, sell stolen data.
GitHub’s own rating also validates claims. It was noted that Saldurgans have a "directly consistent" of 3,800 warehouse numbers. It is necessary not to consider as distributed products; because large tech companies divide infrastructure, vehicleing, CI/CD processes and internal APIs into thousands of small warehouses, the expression "3.800 warehouse" refers to a giant data blog.
How to Fix Nx Console Attachment?
To understand the technique of the attack, you need to know what Nx Console is. Nx is a set of tools used to manage large-scale JavaScript and TypeScript monorepo projects. The Extension allows Visual Studio Code users to perform tasks directly from the editor, such as task execution, visualization of dependency and managing project structure. 2,2 million installations make it one of the standard tools in the developer community.
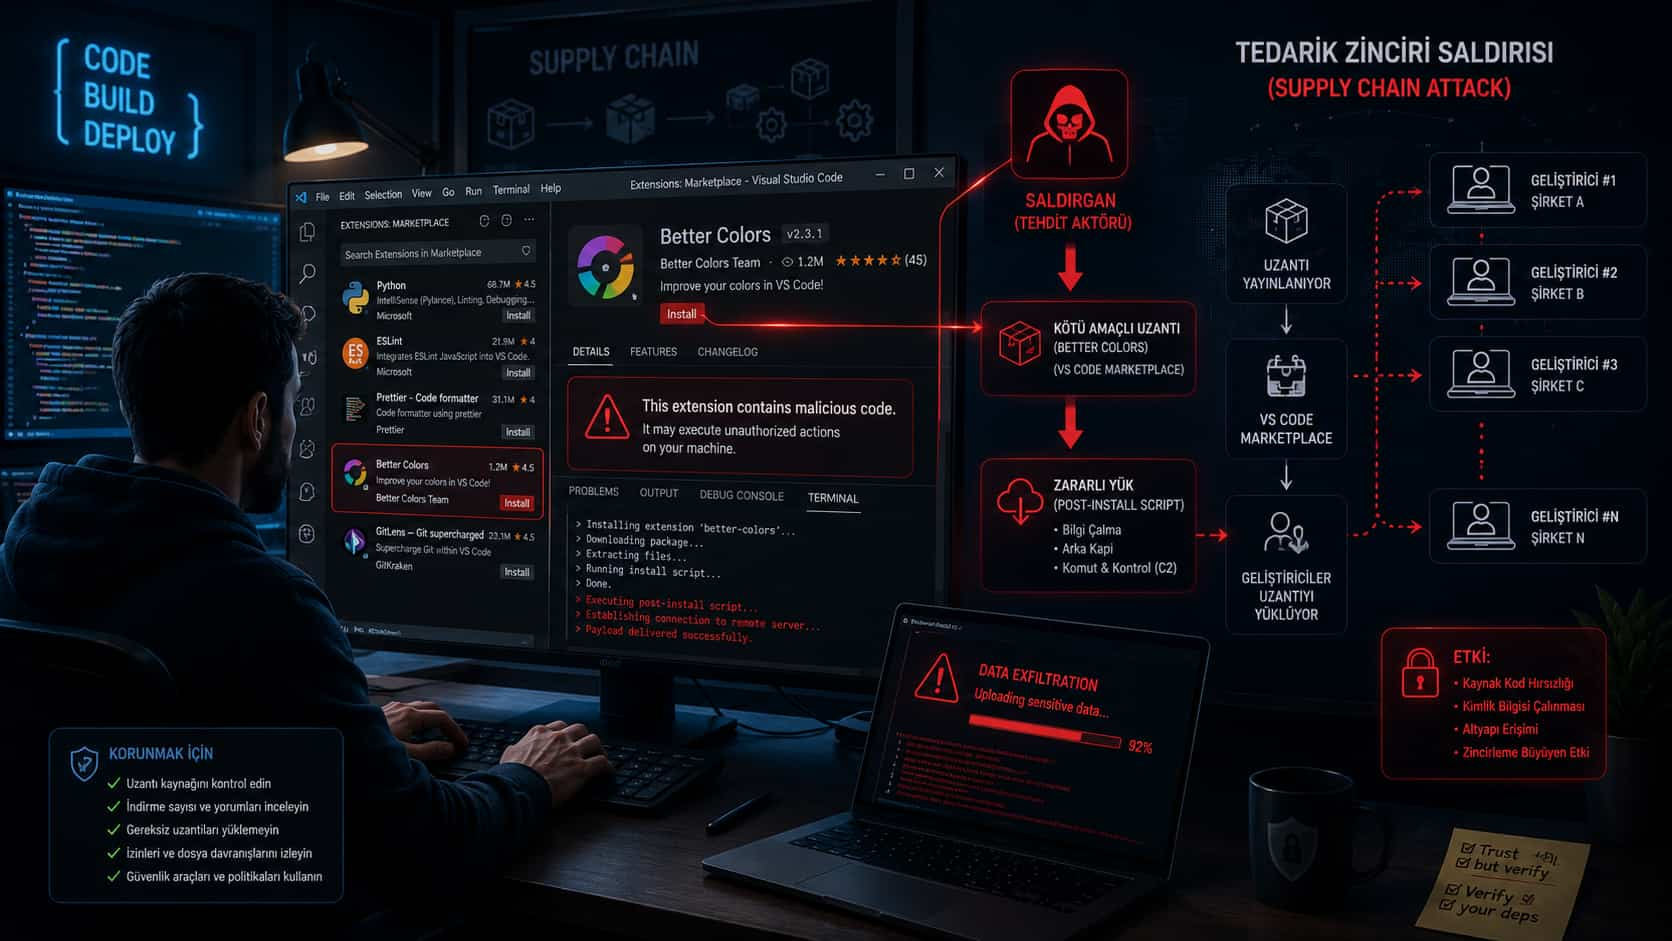
Based on The Hacker News Attacks started to play GitHub token of a contributor. This token was used to send a malicious orphan commit and upload 18.95.0 version to the official market. Shareload inside the published version began to work quietly from the moment it was installed on the device.
The collected data was extremely large. Aikido Security and Home malicious code according to their analysis was aimed at the following list:
Home 1Password cases
Home Anthropic Claude Code configurations
• npm ID information Home
Home GitHub Personal Access Token
Home Amazon Web Services access switches
Home CI/CD system identification information Home
Permanent access to macOS systems was also reported. When the machine of a short developer was handled, the door opened to the entire cloud infrastructure and code warehouses of that person was discussed.
Why is VS Code extensions a dangerous vector? Because a extension works at the same authorization level with the user. There is access to local files, terminal, authentication tokens and cloud tools. Microsoft implements various security measures; but developers install third-party extensions routinely for debugging, automation, artificial intelligence coding assistance and workflow integration. This habit offers an open passage to attackers.
Who is TeamPCP and What is Mini Shai-Hulud?
Help Net Security’s report TeamPCP is defined as a cybercrime group that is followed by the UNC6780 code by Google Threat Intelligence, aimed at open source security tools and artificial intelligence interlayer software. Key tool that allows the group to scale operations: Mini Shai-Hulud.
Mini Shai-Hulud is the version of Shai-Hulud, a self-producing worm documented for the first time in 2025. The function of the worm is to greatly automate the supply chain attacks. CI/CD broadcasts infected versions of other packages, which can bypass other goals from one goal. Hunt.ioAccording to the infrastructure analysis of the group C2 (comuta and control) servers seem consistent in the sub network of 83.142.209.0/24 since March 2026.
Trend Micro’s report The group was determined that at least seven verified waves in 2026. Operations continue without stopping; both compression and data sale strategies are using simultaneously.
2026 Frog List of TeamPCP
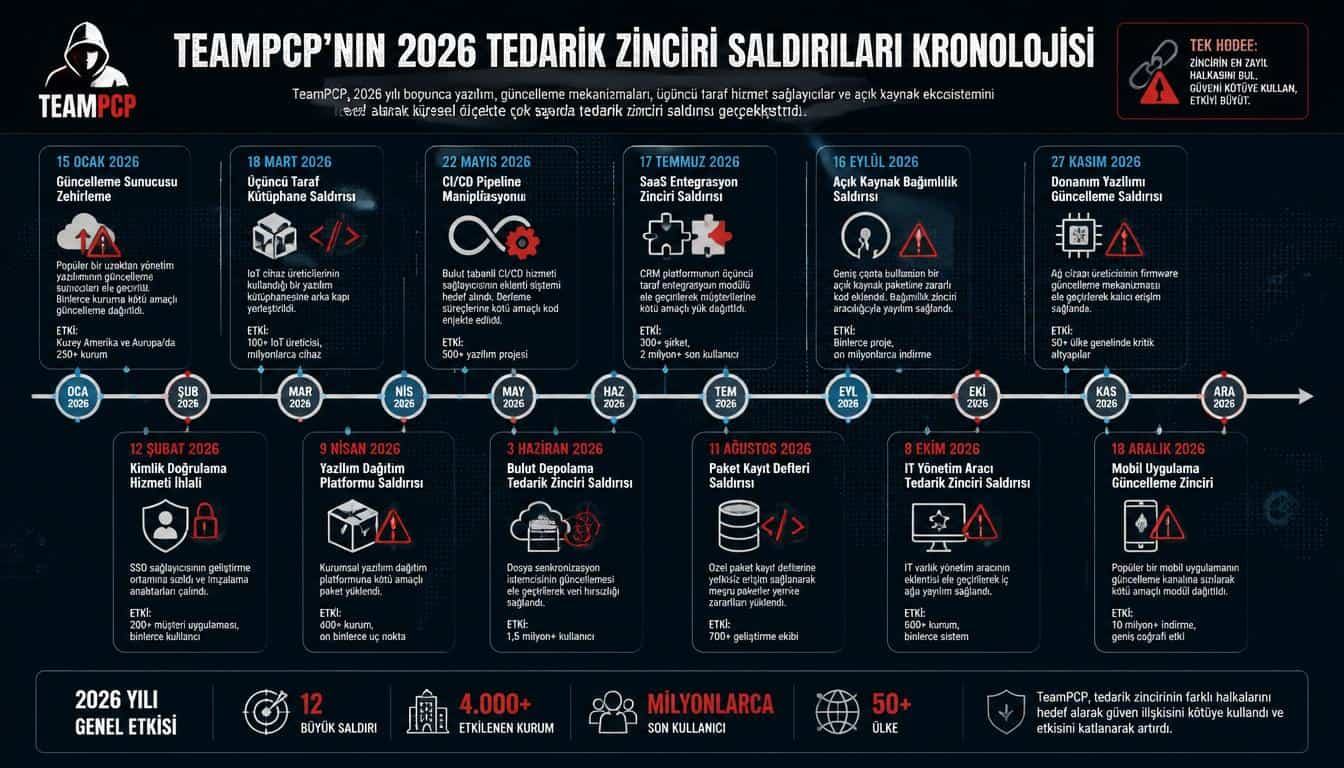
GitHub is not the first big goal of this group. According to the news of VentureBeat Five separate supply chain surfaces were successfully handled in a time frame of only 48 hours. The corrected operations that the group took over 2026 are clearly understood when the size of the table is poured into the table.
Home | Date | Effect | Fidye/Talep |
|---|---|---|---|
Aqua Trivy | March 2026 | Security scanner captured | Not Know |
Checkmarx KICS | March 2026 | CI/CD stolen credentials | Not Know |
LiteLLM / Telnyx SDK | April 2026 | Artificial intelligence interlayer infected | Not Know |
Bitwarden CLI | May 2026 | Password manager vector | Not Know |
TanStack | 11 May 2026 | OpenAI 2 rotates device and code signing certificates | Not Know |
Mistral AI | 12 May 2026 | 1 device, 5 GB source code | $25,000 |
GitHub (Nx Console) | 18-20 May 2026 | 3.800 internal warehouse | 50,000 dollars |
OpenAI’s TanStack attack is particularly remarkable. Two employees were captured and iOS had to rotate Windows code signing certificates with macOS. Mistral AI encounters a ransom message that requested $25,000.
Why are Developer Tools Worth It?
Aikido SecurityDeveloper Relations specialist Mackenzie Jackson clearly summarizes the blind point of security teams in the description given Hackread:
"The future workstations are currently the first goal of supply chain attacks and exactly that's why. TeamPCP hit Trivy, Checkmarx, Bitwarden CLI, TanStack and GitHub now; all through developer tools. A single VS Code extension in one employee’s machine was enough to access 3800 internal GitHub storage. Most of the security teams have zero visibility on what extensions are installed in the developers’ machines or when they are released. Attacks are using this blind spot. "
Ask Jackson described. A developer’s business station is typically home to a large number of highly authorized tools: CLI tools for cloud environments, Personal Access Tokens that provide access to CI/CD pipelines. The authorization to write to these source code warehouses and direct access to production infrastructure is added. All this works at the same authorization level with a VS Code extension.
Artificial intelligence agents and automation life cycle of extensions similar to discussions, much faster than traditional software review processes. A package can broadcast multiple versions per day; security scans cannot keep foot to this tempo. The malicious version in the Nx Console case was only 11-18 minutes active, but this window was enough to reach thousands of users.
Artificial intelligence security risks Home The situation is even clear when evaluated in the framework. The minimum authorization principle in supply chain security opens is discussed for a long time, the necessity of independent audit and monitoring mechanisms. GitHub event sits on a concrete case.
Is It Possible to Protect Developer Environment?
GitHub may seem inevitable. Not. Several practical steps significantly increase resistance to attacks in this category.
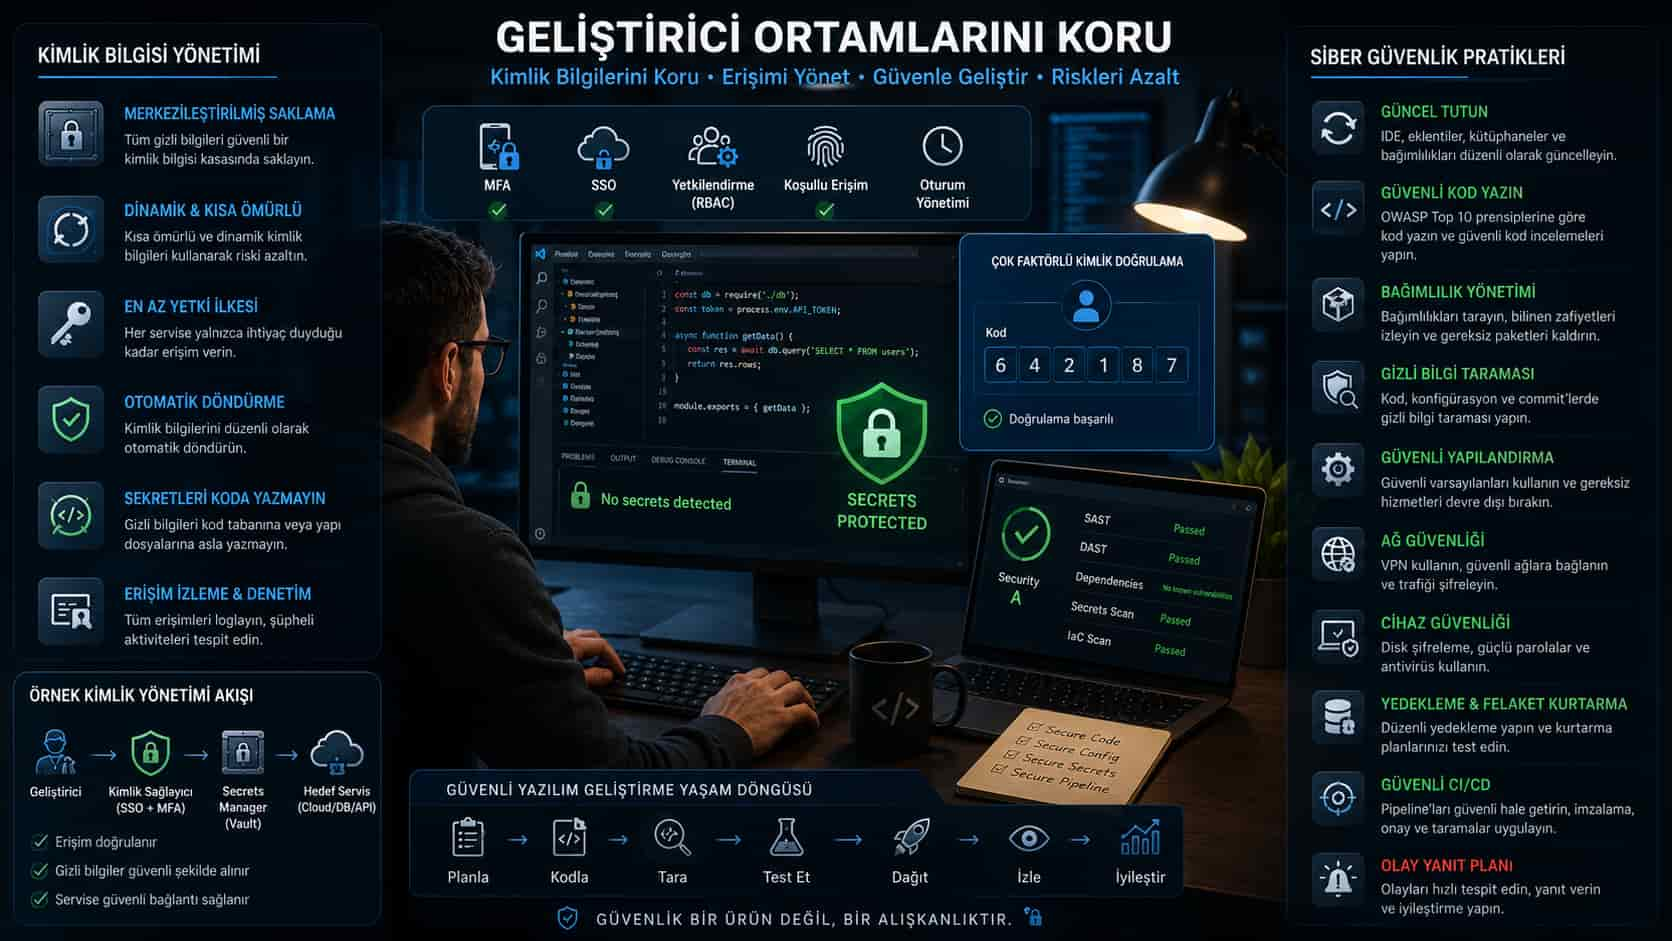
The first step to check the extension. Knowing which VS Code extensions are installed on the machine of developers in the institution, the most basic way to provide visibility. Artificial intelligence coding tools and integrations great convenience; but each new extension means a surface expansion. Keeping a list of approved extensions throughout the institution, it keeps the surface under control.
The second critical field of identification information management. GitHub’s response to breach revealed something: the return capacity is the priority of the surviving institutions. Personal Access Token is short-life of API switches and cloud identification information, it limits damage after a breach. Long life, high authorized tokens remain as one point fault.
CI/CD insulation third size. Separation Pipeline ID information from developer devices, isolate runner environments and implement at least authorization principle at pipeline level, the area where the attacker can navigate when a device is captured.
Finally the extension publisher verification and signature control. Microsoft adds signature verification mechanisms to VS Code Marketplace, but when a contribution is stolen, these mechanisms can be skipped. See how reliable the verified broadcast status appears, no label final evidence is counted in zero trust architecture.
What does the community think?
Supporters
The security community states that GitHub’s response to the event is positive, as well as on the industry standard of the company’s statement. The affected device was agreed to isolate the same day and rotate the credentials for the night. The fact that the customer data is not affected is clearly reported that many large companies have a transparency that they are avoiding even days after the incident. Tom’s Hardware also appreciates a reader’s head: it states that the event’s supply chain attack is getting rid of confused by a large number of users.
News
Critical sounds on the other hand are also strong. The most common point of security researchers is: the employee of a platform, which can be counted in the center of the software development infrastructure in the world, was able to access 3,800 internal warehouse by establishing an extension that does not matter the smallest. This is a structural problem. The trust chain from Endpoint to internal infrastructure should not be so fragile. In addition, the attack series from Trivy for 2026 of TeamPCP was on the day, but the interest for developer tools was expected to turn into this denial concrete damage. Some voice-making security accounts highlight that large-tech companies are still not a systematic mechanisms to control installed tools for developer machines.
Frequently Asked Questions
Who is the TeamPCP group, and who has previously targeted?
TeamPCP is defined as a cybercrime group followed by the UNC6780 code by Google Threat Intelligence. Group targets open source security tools and artificial intelligence interlayer software. Aqua Trivy in 2026, Checkmarx KICS, LiteLLM, Bitwarden CLI, TanStack, Mistral AI and GitHub. Mini Shai-Hulud scales its operations with its vending worm tool.
What version of the Nx Console was affected and when removed?
The 18.95.0 version of the Nx Console Visual Studio Code extension was active on May 18, 2026, at 12:30-12:48 UTC range VS Code Marketplace. The malicious version was removed by Nx team in 11-18 minutes. Nx team went to 18.100.0 and later versions.
Does GitHub be stolen from attacks of internal warehouses?
GitHub announced that user and customer data are not affected. The attack has only aimed at the internal infrastructure, distribution tools, internal APIs and warehouses of unpublished product features. Public GitHub warehouses or private warehouses of customers were not affected by this breach.
Why is VS Code extensions a dangerous attack vector?
VS Code extensions work at the same authorization level with the user. There is access to local file system, terminal, authentication tokens and cloud tools. Since developers build third-party extensions routinely for the help of debugging, automation and artificial intelligence coding, this ecosystem creates a constantly growing attack surface.
What can developers do to protect from such attacks?
The first step to keep a list of approved VS Code extensions across the institution. Personal Access Token and API switches are short-life and least authorized, playing decisive role in limiting damage. CI/CD identification information is included in the developer devices and the security of the accounts where the extension publishers are registered is also among practical measures.
As of May 2026, the speed of TeamPCP did not fall. The group shared the source code of the Mini Shai-Hulud worm by organizing a 1,000 Monero award-winning supply chain attack contest in BreachForums after days from GitHub breach. The new actors will be marked in the next weeks that they will not perform their attacks with the same means.
AdminGoogle ve Samsung’dan Yeni Nesil Akıllı Gözlük Devrimi
Nvidia AI Hissesi İçin Kritik Kazanç Günü Yaklaşıyor


