



North Korea Deepfake Programmer Operation u
Automatically translated
 Admin
A Atlanta start-up lost more than one million dollars, and the thing that arises after three years of pass was not an ordinaryft: a global operation carried out by the state hand. The fake software scheme of North Korea affected 309 US company through a single laptop farm and more than 17 million dollars were transferred to regime. In this article, the five-step mechanics of the scheme are addressing a concrete protection guide for deepfake interview tests and HR teams.
Contents
The article consists of nine parts. The beginner reader can pass to practical guide for HR directly.
How to steam a start-up in Atlanta a million dollar
The global size of the operation and why it remains invisible
Operatifler actually who: cultural test and self- hacking operatif
Five-step operation, from the production of ID to leak from inside
They do not blood the camera, they change the camera
KnowBe4 example: the security firm was even blood
Pindrop sample: The detection company itself became the target
Practical deepfake protection guide for HR Home
This is just worth North Korea problem l
A Start-up in Atlanta A Million Dollar
December 2020. Marlon Williams, founder of Starter Labs, a small blockchain start-up in Atlanta, met with a new one in a Telegram group where crypto developers are installed. On the contrary, the person had introduced himself "Pembra Sherpa". The profile was smooth, the messages were streamlined, the code sent was cleaned. She was an ordinary dating for Williams with more than twenty years of sector experience. In fact, it was the first step of a trap.
Williams gave a few small jobs, he was satisfied with the result. More responsibilities came, then a little more. This patient climbed for months; at the end of the developer, a reliable wasme, which can access the smart contracts of Starter Labs, even the technical leadership. Williams relied on him.
Then a day, with the access it gives confidence, the source code of smart contracts evaporated $740.000.
Williams was still online and refused to accuse the party against the phone, said it was not a reason for him to pay well and play. After a short time, shots from other wallets were understood. According to Williams’s own statement, total loss exceeded a million dollars in three separate events. Coins have passed a mixer service called Tornado Cash, used to hide criminal crypto streams and the trace was lost. The developers and advisers hired with digital traces and disappeared.
She knew she was a scam of her from per Williams. But who, why and how, the answer to these questions remained open for three years.
FBI in 2025 brought the fact to Williams. "Pembra Sherpa" has never been. Four names in Iddianame Kim Kwang Jin, Kang Tae Bok, Jong Pong Ju and Chang Nam Il. The team went to the United Arab Emirates in 2019 with North Korean travel documents, there they prepared fake IDs. All of whom were part of a remote IT workers program conducted by the state hand in the control of Jong Un regime.
Georgia North Regional Federal Court on June 24, 2025, The U.S. Department of Justice announced In the scope of a five-factor claim, telecommunication scam and black money laundering accused of conspiracy. The amount that was stolen in the iddianame was over 900.000 dollars. Saver Theodore Hertzberg stressed that this case creates a self-confident threat for companies running remote IT workers. She was like a movie while telling her best per Williams, she said you’ve seen things on the screen only. The incident was one of the few victims who share with the public; Based on Hypepotamus Instead of staying behind the curtain, the effect of speech was heavy bass from the personal preference and shared the best as a warning.
But Williams’s story wasn’t a movie. It was a part of the agenda of a system. And that system is at least once leaked to almost all of the Fortune 500 list. Currently, thousands of engineers are sitting at a Zoom interview next to the world. Some of them had no sided face to the camera.
The Size of the Operation Not A Level
Williams may seem like an isolated misfortunate. The numbers say the opposite.
The number of companies released has increased rapidly in the last year. Baro Union of New York According to May 2026 analysis The number of victims are expressed by the faces in the prosecution of US authorities. According to the estimates of the United Nations, the regime gets hundreds of millions of dollars per year. A real cash flow in a single pen for a country crushed under constructions.
But this is not just a win that consists of salaries. In February 2025, crypto exchange Bybit suffered a hack of $1.5 billion at once. According to the report of TRM Labs, North Korea only played $1.6 billion in the first half of 2025, which coincides about 70 percent of the global cryptocurrency. A large part of these burglars took place from inside, placing operatives that act as they live in another country.
So Williams’s story is not only a bad coincidence. A small part of a whole economic structure.
Stunning, which companies are affected. Charles Carmakal, the head-tech controller of Mandiant, clearly summarized the situation at a press conference in 2025:
"You're literally in the hands of every Fortune 500 company, if not hundreds of, there are dozens of applications from North Korean IT workers." (Charles Carmakal, Mandiant)
The more life-consuming part that Carmakal adds was: almost all of the information technologies that he spoke with him, had agreed that they hired almost a few dozen people.
The most known example of scissor is Christina Chapman's laptop farm run from the house in Arizona. A ball-5 among operatives employed through this operation according to the description of the US Ministry of Justice TV network, a Silicon Valley technology firm, a aerospace manufacturer, a US car manufacturer, a luxury retail store and a US media and entertainment company. The only name to the public is Nike; According to the detection of Fortune magazine, the company paid about 75,000 dollars to an operatif using stolen identity.
When Gartner comes to 2028 according to an estimate, one of the four business applications worldwide may be fake. When this figure was first heard, most people were exaggerated. When we look at today, Mandiant’s hand is learned to be hundreds of applications from every Fortune 500 company, it stands modestly.
Why? The response is not complicated. The United Nations sanctions have closed the gate of the global finance system to regime. Operatifler is transferring the large part of the salary they receive, to Pyongyang, some steal the resource code, customer data and crypto wallets of companies they skip a deeper step. The U.S. Treasury has a clear message of the Foreign Assets Control Office (OFAC): paying a North Korean operatife salary, even without knowing at all, the breach of sanction is considered. So companies like Williams lose twice: their money first, then their legal security.
That’s why it’s invisible: shame. Most of the affected companies can not disclose the event to the public. The explanations not only protect their reputation, but also melts the risk of federal investigation. That’s why it’s important to clearly share the story of a few people like Williams: because the rests are silent, and silence are the biggest allies of this operation.
Behind Curtains: Who Is Operatifler Actually?
When the number of operations are discussed, the question comes: who are thousands of people? The answer fits neither the state agent stereotype nor a simple criminal organization.
Stimson Center released on 38 North platforms based on analysisIn case of qualified computer engineers and small teams grown by operatifler regimen, it is mainly placed in Russia with China. There are internet access in places where they stay, unlike most of their citizens. This is offered as a privilege for regime; if in reality, it is part of the work jealous. The sale of broker companies, fake account-generating brokers and pre-approved freelance accounts is in the case it turned this settlement into a sector.
U.S. Department of Foreign Affairs Human Leakage Report openly mentioning the issue: Northern Korean workers who are sent abroad are kept under forced operating conditions, the large part of their salary (the average 70 percent according to therapors) is transferred directly to accounts in state control and they are punished if they cannot hold their earnings goals. The remaining families are a printing tool. So the same person is the perpetrator of both global cybercrime economy, and a citizen that the state squeezed.
Paradoks: The only size bad man image from mind when it is called North Korean operatif, the fact does not reflect full. Is Operatiflers evil with their own consent, or is part of a work that has been forced? Answer two: responsible for law, ethically tangible, human size trajik.
Kim Jong Unfair Test
This double trap of Operatifs an interesting detection opportunity to defend the defending side. Man Meyers, Chief Intelligence Officer of Crowd Konferansı, spoke about a cultural test technique that circulates in the 2025 RSA Conference: asking him to insult Kim Jong Un to understand whether a candidate is really North Korean. Because insult the manager in North Korea, a crime that can result in severe punishment of the family. Operatif cannot remove this sentence from the mouth.
In April 2026, this test moved to the real world in an interview clip viral on social media. She wants to say a phrase that insults Kim Jong Un from the interviewer candidate on the clip; the candidate pauses, cakes and eventually ends the interview. Although the incident turns into a mime, the technique behind is serious: even the most advanced real-time deepfake tool, this cultural close does not stage. Because there are visual and auditor synthesizers, but the man using deepfake is North Korean, and he can not get this sentence into the mouth.
Operatif Self Hacked
Human size showed itself more than another edge of the scene. December 2025 threatened intelligence firm Flashpoint, revealing a case shared with the public. Ironically: an operatif, who smeared malware for many years, was infected with its own machine with a common knowledge-unique malicious (LummaC2 type infostealer). Designed to steal passwords of ordinary users, it was harmful, that time a state actor poured into all digital footprint analysts.
The persona who watched Flashpoint as "Trevor Greer" was a tool bag, not a person. Logs that came into show a GitHub account with a fake commit history that dates back to years ago, a variety of freelance platform accounts, independent fake IDs from each other, "BlockBounce". All of a single operation, which lasts parallel lives on multiple platforms, turned back to a single indefinite.
Trevor Greer case is small but symbolic. At the point where the operation is technically developed, what makes it fails, a state actor was an ordinary consumer pest, running on his own machine.
How Does Five Step Operation Work?
On the back of a case like Williams, there are more than a single CV sent. This is not the work of a person, a production line: every step is standardized from the production of ID to reach Pyongyang. The "Jasper Sleet" report, published in June 2025 of Microsoft Threat Intelligence, Palo Alto Unit 42's April 2025 research and the Wagemole work of Okta Threat Intelligence in September 2025, document every ring of this line.
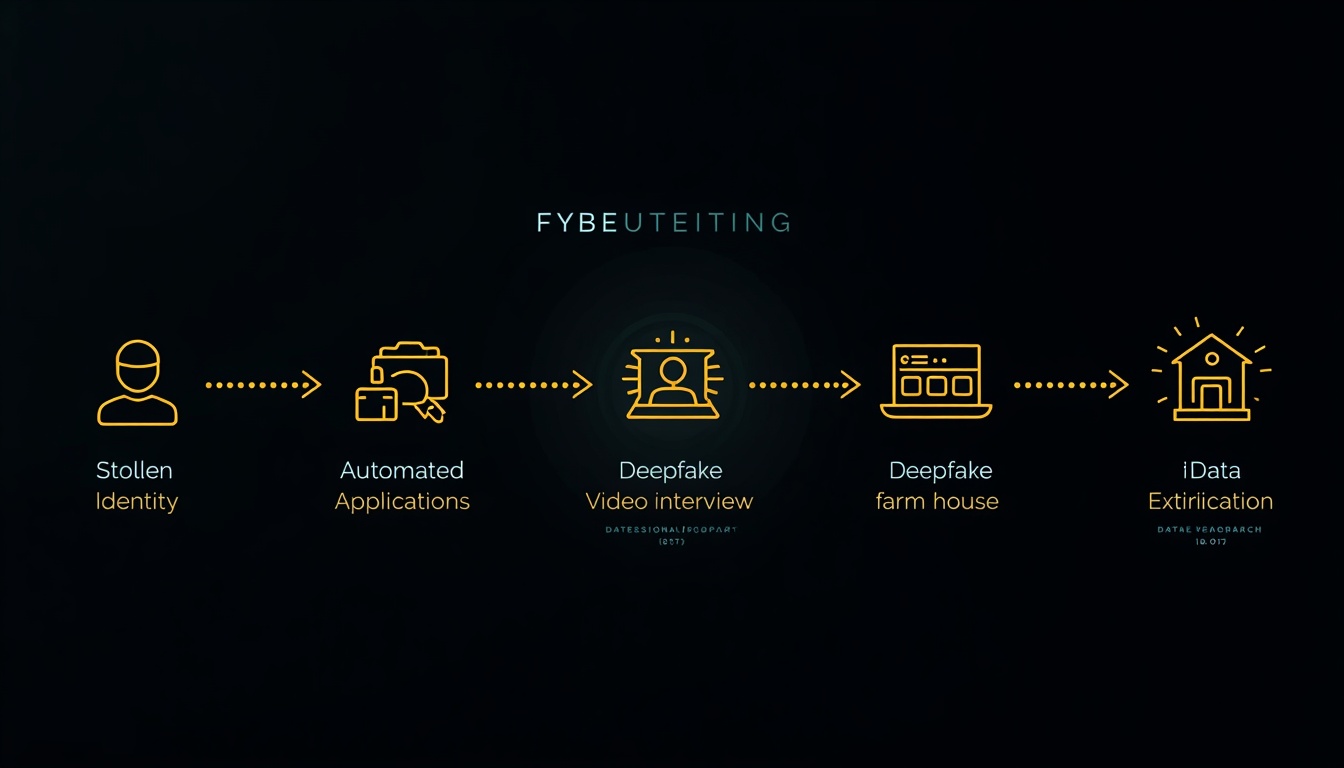
1. Step, Identity Production: Everything starts with personal data of a American citizen stolen: social security number, driving license information, address history. These are already sold in the black market for years, the regime uses the current dark market. Then the actual photo of the operatifin is placed with artificial intelligence tools instead of the photo of the stolen ID; the same photo turns into the visual of a LinkedIn profile. After here is a reputation architecture: fake commit pasts, which appear to extend years ago in GitHub, the verified freelance business history, referenced to each other. More than 130 actors in Okta’s research documented about 6.500 interviews with 500 different companies. So the system is not a once-time trick, a factory that produces unlimited number of realistic applications.
2. 2. Step, Mirror Minister Mirror: The most surprising detail of the operation in this step. Ordinary expectation was to scan the job ads of operatifs and produce CVs with artificial intelligence. All of them are correct. But the main mechanical more sophisticated that Okta reveals: operatifler publishes fake ads similar to the real job pros of target companies through cash companies, collecting applications of real candidates. Then by analyzing these real CVs, the application is from the tracking systems (ATS), which words learn what formats pass, and their fake materials are set accordingly. So a ATS system running artificial intelligence filter on the defense side is aggressive without realizing their actual test driving. The March 2026 report of Microsoft Threat Intelligence calls this cycle as artificial intelligence in every ring of the attack life cycle. The mirror that looks at the mirror is in place: a defense set up with artificial intelligence, a trained attack with artificial intelligence.
3. Step, Deepfake Interview: Once you have passed the CV front, the sequence comes to video interview, and here three technologies work simultaneously: real-time face change, sound masking and an artificial intelligence suflector. Stimson Center’s February 2026 report is a remarkable detection on the audio side: it was observed that the operatifs from the third quarter of 2025 began to widely use noise blocking software that suppress the tools and media sounds that convert the audio to the female profile. Home AI sound clone technology Home shows the point it reaches. Live support if at least noticeable layer. Operatif is not alone: on a screen that does not appear in the image, the question of the interviewer is translated into real-time subtitle, a language model will read this question and produce the appropriate answer and proposes operatife. So when the person responds to the question, another artificial intelligence pushes the answer to the ear.
4. Step, Laptop Farm: The interview was passed, the candidate was hired. The company cargoes the corporate laptop to Arizona of the new employee. He was the house of the 50-year-old Christina Marie Chapman in a quiet suburb called Litchfield Park. Chapman agreed with one who recommends himself as a US face on LinkedIn in 2020. In 2023, when FBI was looking for, he handed over 90 companies in his laptop; there were little notes that each of which belong to the company next to and which had been associated with stolen identity. Chapman kept these laptops open for three years, connecting to the local internet, if necessary, cargoed abroad (at least 49 sent to a city on the North Korean border with China), holding and transferring payments with stolen IDs.
Based on the disclosure of the US Ministry of Justice Judgment Randolph D on July 24, 2025. Moss convicted Chapman for 102 months (8,5 years). Figures in the decision are clear: 309 US companies were impressed, 68 Americans were stolen, and over 17 million dollars revenues were transferred to the North Korean regime. Chapman’s defense stated that he initially understood the illegality of him and maintained to meet the costs of his mother who had undergone cancer treatment; the judge rejected this nuance completely, but the result was not changed. Chapman was not alone. In February 2026, Ukrainian Oleksandr Didenko received a prison sentence of Wang brothers with New Jersey in April 2026. In the event of the "DPRK RevGen" initiative of the Ministry of Justice, the coordinated prosecution for the facilitator network in the US territory since March 2024.
5. Step, Access from inside: Everything is prepared here. Business starts now. Operatif connects to the laptop remotely, typically through a VPN, a shift that fits your local time. Working shape two layers. The first visible job: to answer the team’s Slack, complete small tasks, maintain a good remote employee impression; here also helps artificial intelligence. Second invisible layer: Establishing remote management tools like AnyDesk and RustDesk quietly, leaking customer data, source code and intellectual property through SharePoint and Git warehouses. In particular, the operatif in the crypto industry is waiting to be able to touch the wallet keys safely gained, then Williams is a kind of movement that lives. Microsoft’s April 2026 report draws particularly attention to a telemetry signal: if a new employee is often triggered the alarms of "unimous travel" in the first two months, that is, if the morning is connected from Texas, in the afternoon from Beijing IP, this is no longer neglectable indicator.
Here’s five-layers, coordinated mechanical that are under the process that Williams’s film was saying. In the next chapter, this mechanics look at the technical heart, namely what the camera does.
They don’t Blood the camera, They Change the Camera
The classic advice to stop deepfake instantly was the same for years: ask for a sudden movement from the candidate. Remove three fingers in front of the face, turn on his head, stand up. Because early term deepfake software was a fake facial systems on a real camera image; the facial tracking algorithm in sudden motion is broken, the pixelation appears on the edges of the fake face, revealing the stitch between the real face and fake face.
There was a period that this test works. It’s over time, and because most of the interviewers still do not know a architectural change.
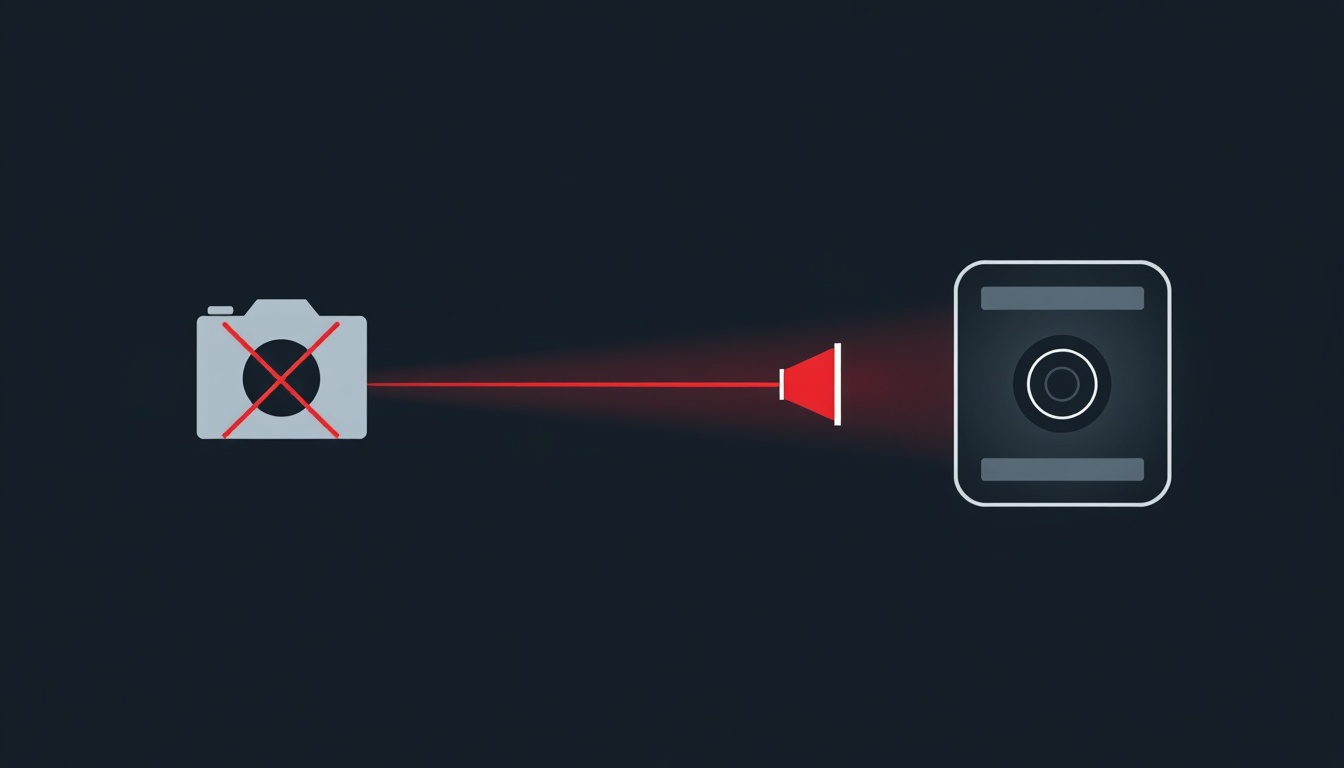
The old logic was: the camera attracts the real face, the software captures this image, over which another face gets the mask, then reflects Zoom. The fragile ring of this chain was the moment of capture; the facial follow-up on the sudden movement is delayed, the mask was lost. Three-finger test was exploited full brittleness.
Today’s attacks work with a different architecture. The main idea is: instead of changing the data sent by the real camera, they change the camera itself. The name of the technique injection attack (injection attack). A virtual camera device is introduced to the operating system via free broadcast software or virtual camera add-ons like OBS Studio. Zoom or Teams are asked which camera will be used. Saldurgan chooses its virtual camera, not the real camera from that list. If the output of the virtual camera is pre-made or real-time produced deepfake video stream.
The result is: the system no longer sees the signal that camera does not work, because the camera really works, not only a real camera. Motion tests are also not working, because the movement is also manufactured into the deepfactor flow. Three fingers are getting out of the face, but that three fingers are also synthetic.
Biometric authentication company iProov Based on 2025 threat report 2,665 percent of virtual camera attacks in a year, the face change (face-swap) attacks increased 300 percent. Virtual camera attacks have become the primary threat vector and moved to mobile devices because of tools that are partially leaked into application stores.
What is the Solution?
If the sudden motion test crashes, what is going back? IProov’s answer to measure physical response. Patented Flashmark technology works with logic: the screen of the device reflects a random color sequence for a short time to the user’s face, so the color paterni of the back reflected light is sent to the cloud and the system controls that the pater matches and matches with the expected ranking. The color sequence can not be single-use and pre-predictable every time; it is not possible to know that an attacker is expected.
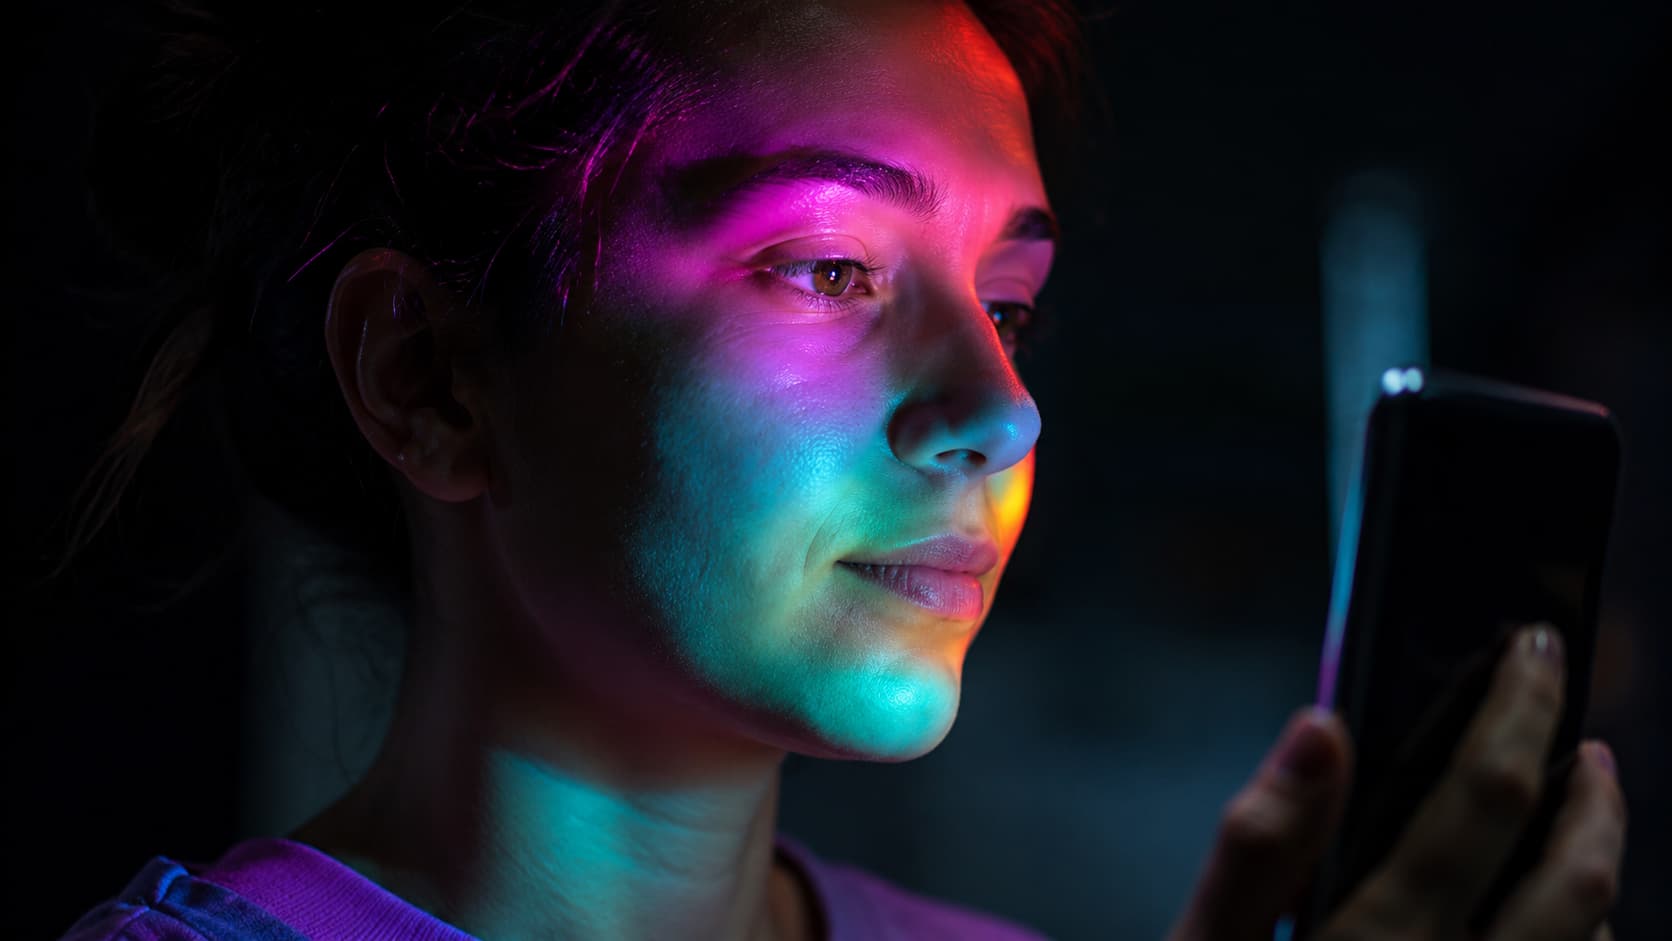
Manik is based on: physical response to the light on a real face screen, skin color and glare change. A virtual camera stream can’t produce it, because it’s an already pre-crafted image of the flow; it doesn’t have the capacity to synthesize the response of the momentary face. Method passive: the user does not do anything, just looking at the screen.
Here you need a warning. Technologies such as Flashmark seriously push injection attacks, but do not finish. Operatifler and actors that mimic them, examine and adapt every new layer of defense in a short time. There is a fact that the experienced researchers of the field repeat: how much investment is done to defend, the manufacturer models always go ahead.
The summary of this section is: three fingers test died, the virtual camera attack has become common, the new generation solutions that measure light-thepki come. But even these solutions aren’t enough on them. The camera is now unreliable witness; it is necessary to call other witnesses. Home protection against deepfake of video-based authentication processesIt is not a single layer today, but it is addressed with a very model approach.
KnowBe4 Case: Safety Company Known
If you need to choose the highest company that is likely to capture the North Korean deepfake interview scheme, then it would be KnowBe4 one of the first future names to mind. Florida-based company has the only job: teach employees to recognize their social engineering attacks. That’s what the company sells daily, you’d like to know that one like Williams has already learned.
KnowBe4 was also blooded.
The person who shared the incident with the public in July 2024 was Stu Sjouwerman, CEO of KnowBe4. Your own blog I chose to tell, that the decision was not unusual in the cybersecurity world: most companies hide such events, KnowBe4 reversed.
The company has announced for a software engineer position and processed a standard process: CV review, reference control, past verification and four separate video interviews. The candidate passed every stage. Fake U.S. ID was placed in a photo developed by artificial intelligence to the background of a stolen American citizen. Then he applied the company rule: a Mac laptop was shipped to the house of the new employee. The address was a laptop farm, which was seen in Christina Chapman case.
Laptop unopened KnowBe4’s endpoint detection and interference (EDR) software triggered alarm. The device started to install a information-unfortunate malicious; the method was carried out from a Raspberry Pi (credit card size, cheap and programmable mini computer) that is physically connected to the laptop. EDR software captures the event about 25 minutes after the opening of the laptop and isolated the security team device.
KnowBe4 findings shared with Mandiant and FBI; the candidate was verified to have a North Korean operatif. The company did not leak data to its systems, because the detection occurred in the first real movement of the operatif. The closing sentence of Sjouwerman’s blog post has repeatedly been quoted since that period:
"If you can come to our head, you can almost come to everyone." (Stu Sjouwerman, KnowBe4 CEO)
Cümle stops on the surface as a damp warning. The real more gang in the gold: KnowBe4 did not block recruitment, because each of the four video interview was passed, the past verification turned out clean, the fake identity was so well prepared that the standard HR processes did not signal any step. The company saved something is not an interview control, the next layer; namely EDR. Auction can be passed, the ID can be verified, the references can be approved. And the attacker can still be inside. The important thing will be noticed within few minutes when it comes inside. In the case of KnowBe4, it was 25 minutes; months in the case of Williams. The difference between is how advanced the company is, not how many layers of defense architecture.
Pindrop Example: The Self-targeting of Detection Company
In the case of KnowBe4, a safety training company was ironic. Almost philosophical: a company that sells deepfake capture, faced with a deepfake, who applied to deepfake capture team. Pindrop is a sound biometry and fraud detection company based in Atlanta; for years it is working on whether the voice on the phone really claims. In recent years, the product portfolio was expanded to deepfake detection. The product called Pindrop Pulse for Meetings detects real-time deepfake candidates in Zoom, Teams and Webex meetings. So Pindrop sells the answer of the question how to capture deepfake interview to other companies.
In April 2025, Pindrop has opened an engineering position for its company and over 800 applications in several days. The number itself was suspicious. The company found that more than 100 candidates are completely fake in detail: CVs, manipulated references and live interviews made with artificial intelligence, deepfake technology.
One of them is particularly interested. Candidates said "Ivan X", According to the transfer of Computer Weekly The interview gave three classic signals: the facial expressions were not synchronised with words, the sound was not sitting with the lip movement and was a non-natural delay in a technical question that was not previously prepared, as if the response was paid before and then played. Pindrop refused candidate. CEO Vijay Balasubramaniyan, CEO of the bizarre party, summarized: the candidate was referring to a software engineer position in deepfake detection team.
After eight days, with similar credentials, a second candidate with a different face was applied. Pindrop security assistant marked this interview instantly and saw that the second candidate is more advanced: higher resolution face change, more clear voice, more fluent responses. At the end of IP analysis, both clearly documented North Korean proxy transfers. That’s not an ordinary identity scam, but the state hand-held operation is based on the gate of the detection firm.
Another case at the same time showed that the scheme reaches the gate of small companies. Jason Rebholz is a founding partner and CEO of a artificial intelligence security firm called Evoke Security; one who worked as an incident intervention in his previous career and worked as CISO, has been researched for years on deepfakes. So from people who are theoretically the most difficult blood. In January 2026, a candidate came through a link that knows when the position of security researcher; CV clean, past neat, connection is reliable. There was a feeling inside throughout the interview: this deepfake. But there’s something that stops him: if it comes to a percentage and feels bad if it faces a real candidate? Rebholz did not face the candidate, finished interview and sent the records to a acquaintance, and crossed deepfake detection technology. Confirmed: deepfake.
KnowBe4, Pindrop, Evoke. The most alert companies of the sector were all blooded or almost blooded. The common thing among them is not technological weakness, but a weakness in human and process size. A person had to decide, a process had to take one step, and at that time she offered a ground to withdraw back at all times "the probability of a mislead on the earth." That’s why the part in the row is not an individual alert, the system.
Practical Deepfactor Protection Guide for HR
Those who see here fit for a single sentence: what a single person can stop this attack, what is a single tool. KnowBe4 was not able to capture four interviews, Pindrop caught with the warning of technology, Williams could never capture. The difference was not in alertness, but in process design. This section offers that design: signals that appear first, then layered defense model, then low-tech but effective measures, then the vehicle ecosystem and finally the limits of these vehicles.
Manual Red Flags
Before entering technology, there is a checklist that any HR team can apply without additional budget today. All of the following are FBI, Microsoft, Okta and Mandiant’s signals that pass again in public reports.
The candidate’s contact number is not a real mobile operator, but it is necessary to pay attention if the VoIP or virtual number is registered. If the address at CV does not match the laptop delivery address, it is necessary to suspect; if the candidate said that he lived in Texas and gives another address in Arizona for the laptop, this type of Christina Chapman is a laptop farm sign. An employee who can’t explain the basic concepts in the task of ensuring impressive answers in the interview can use live AI suflor. The same suspicion applies to a candidate that looks strong in GitHub but can’t tell step by step by step.
There are also visual signals. If the background is fixed and artificial, the candidate is born in front of a wall that does not move single pixels for a minute; most deepfake tool works better with fixed background. It is necessary to pay attention if the same photo faces different backgrounds in different CVs; reverse visual search can capture these matches. Finally, if the salary is asked via a crypto or broker account, it is necessary to be in alarm; the work looks legal, but if the payment instruction is out of queue, the flow of money to the regime starts here. None of them are not evidence alone. But the appearance of two or three at the same time is deep control ground.
Five Layer Defense Model
The weakest state of defense to trust a single point of control. KnowBe4 case showed it clear: four interviews were passed, the past verification was clear, the identity was approved, the attacker still entered in and captured him EDR. So not to prevent the function of the defense from entering, creating the chance to capture at every stage.
Home | Home | What to do |
|---|---|---|
1 | Application filter | IP analysis (it comes from the declared country), VoIP detection, cross CV verification (LinkedIn, GitHub and previous employers confirm each other) |
2 | Authentication | Biometric ID and vitality test before contracting; not simple photo matching, a system resistant to injection attacks |
3 | Interview moment | Real-time deepfake detection software and unpredictable questions; software can be bypassed, culturally unenforceable |
4 | Recruitment moment | Physical verification of laptop delivery address, the minimum access principle for the first 30 days, automatic assigns requesting bordro change m |
5 | Continuous monitoring | Re authentication in Critical access, geographical anomaly alarm (importless travel), marking the usual behavior in the first two months of the new employee |
Low Technology, High Effect
Most of the above layers require budget. But a large part of the attack is sensitive to friction (friction). Small steps designed smartly can be more effective than expensive vehicles. Jason Rebholz’s advice is simple and cost-free: run the first week even if the position is remote. One week, a single physical contact, and the operatifin is not able to fly from Pyongyang. In the case a CISO colleague was transferred, the person from the first day ofise was not the interview; a local actor was hired to get operatif laptop. But the actor is one-day, operatif permanent. FBI Recommending companies It suggests that the recruitment and onboarding process is completed to face as much as possible.
There are other low-tech tests that can be applied in the interview. From the candidate to call the camera to rotate 90 degrees or pull from another corner of the table; virtual camera flow is forced to synthesize this new angle. It is also effective to take an object (book, glass, paper) on the background from the candidate and want to keep it close to the face; deepfake tool can not be realistically defined object. Another method to ask questions about spontane about the local details of the city he said. If the old hand shake test is no longer stop most deepfake; that’s still an effective, expected movement of the previously prepared spontane movement. Some major companies have returned to this road: Google, as noted in the May 2026 report of the Baro Union of New York, even for remote roles, the forced face-to-face interview tour was reactivated.
Open Source and Commercial Vehicle Comparison
Most of the vehicles on the market claim 99 percent accuracy. The reliability of these figures in a subhead. First you need to clarify the answer to two questions: what does a tool, and who tested their claims. Due to the same category, the tools are actually doing very different jobs. Some work live during interview, joins the meeting as a boat. Some analyze the recorded video after interview. A part is embedded in the authentication stream. Part is developer API. Some of them are another thing; for example, C2PA does not detect deepfake, sign the originality of the content.
These differences can be read in the following two tables. "vendor-claim" in the independent verification column is the company's own claim; references such as TEM Journal, NPR and iBeta are third-party tests.
Car Rental | Home p | Working Mode | Target Script | Independent Verification |
|---|---|---|---|---|
Deepware Scanner | Open source core, freemium (Turkish firm Zemana, Ankara/Bilkent) | Web upload and API; max. 10 min video, only facial manipulation u | Post-exclusive record analysis, content moderation; live Zoom bot w l |
EfficientNet-B7, GitHub open source; deepfake research since 2018
Bio-ID
Commercial (German, Fraunhofer IIS origin)
API and SDK, free browser playground
KYC, authentication streams (not a friendly interview tool)
TUV and iBeta PAD certificates; high score in academic benchmark tests
SBI (Self-Blended Images)
Open source (akademic, GitHub)
Python library; you need to integrate it into your own system
Research, corporate integration, academic comparison
Academic literature is one of the strongest open source foundations Home
DeepFake-o-meter
Open platform (UB Media Forensics Lab, academic)
Upload video URL or file to the website
Single video analysis, academic usage, multiple algorithm comparison
University guarantee; transparent cross test with multiple algorithms
C2PA / Content Credentials
Open standard (Adobe, Microsoft, BBC, Intel installed)
Adds cryptographic signatures to metadata of content
Content originality and provenance; does not detect deepfake
Open, royalty-free standard; large member base
Deepware Scanner, the first place in the table, is a Turkish cybersecurity company called Bilkent Cyberpark based Zemana in Ankara. Important distinction: Deepware is not a Zoom plugin, a video forensic tool. After the record of the contract you upload and analyze, it does not work in real time. Web browser browser.deepware.ai free access. A quick and cost-free domestic starting point to train the team.
Car Rental | Working Mode | Target Script | Independent Verification |
|---|---|---|---|
iProov Dynamic Liveness | API and SDK reflects random color array from screen to face with mobile and web; Flashmark | Authentication and KYC before contracting, high security | NIST SP 800-63-4 compliant; iBeta PAD; CEN/TS 18099 High and Ingenium Level 4 injection tests Home |
Pindrop Pulse for Meetings |
AdminOpenAI Yapay Zekanın Yönetiminde Üç Adımlı Plan Sundu
Yapay Zeka Çağında Kamu Siber Güvenliği Alarm Veriyor


